Appearance
Audit log
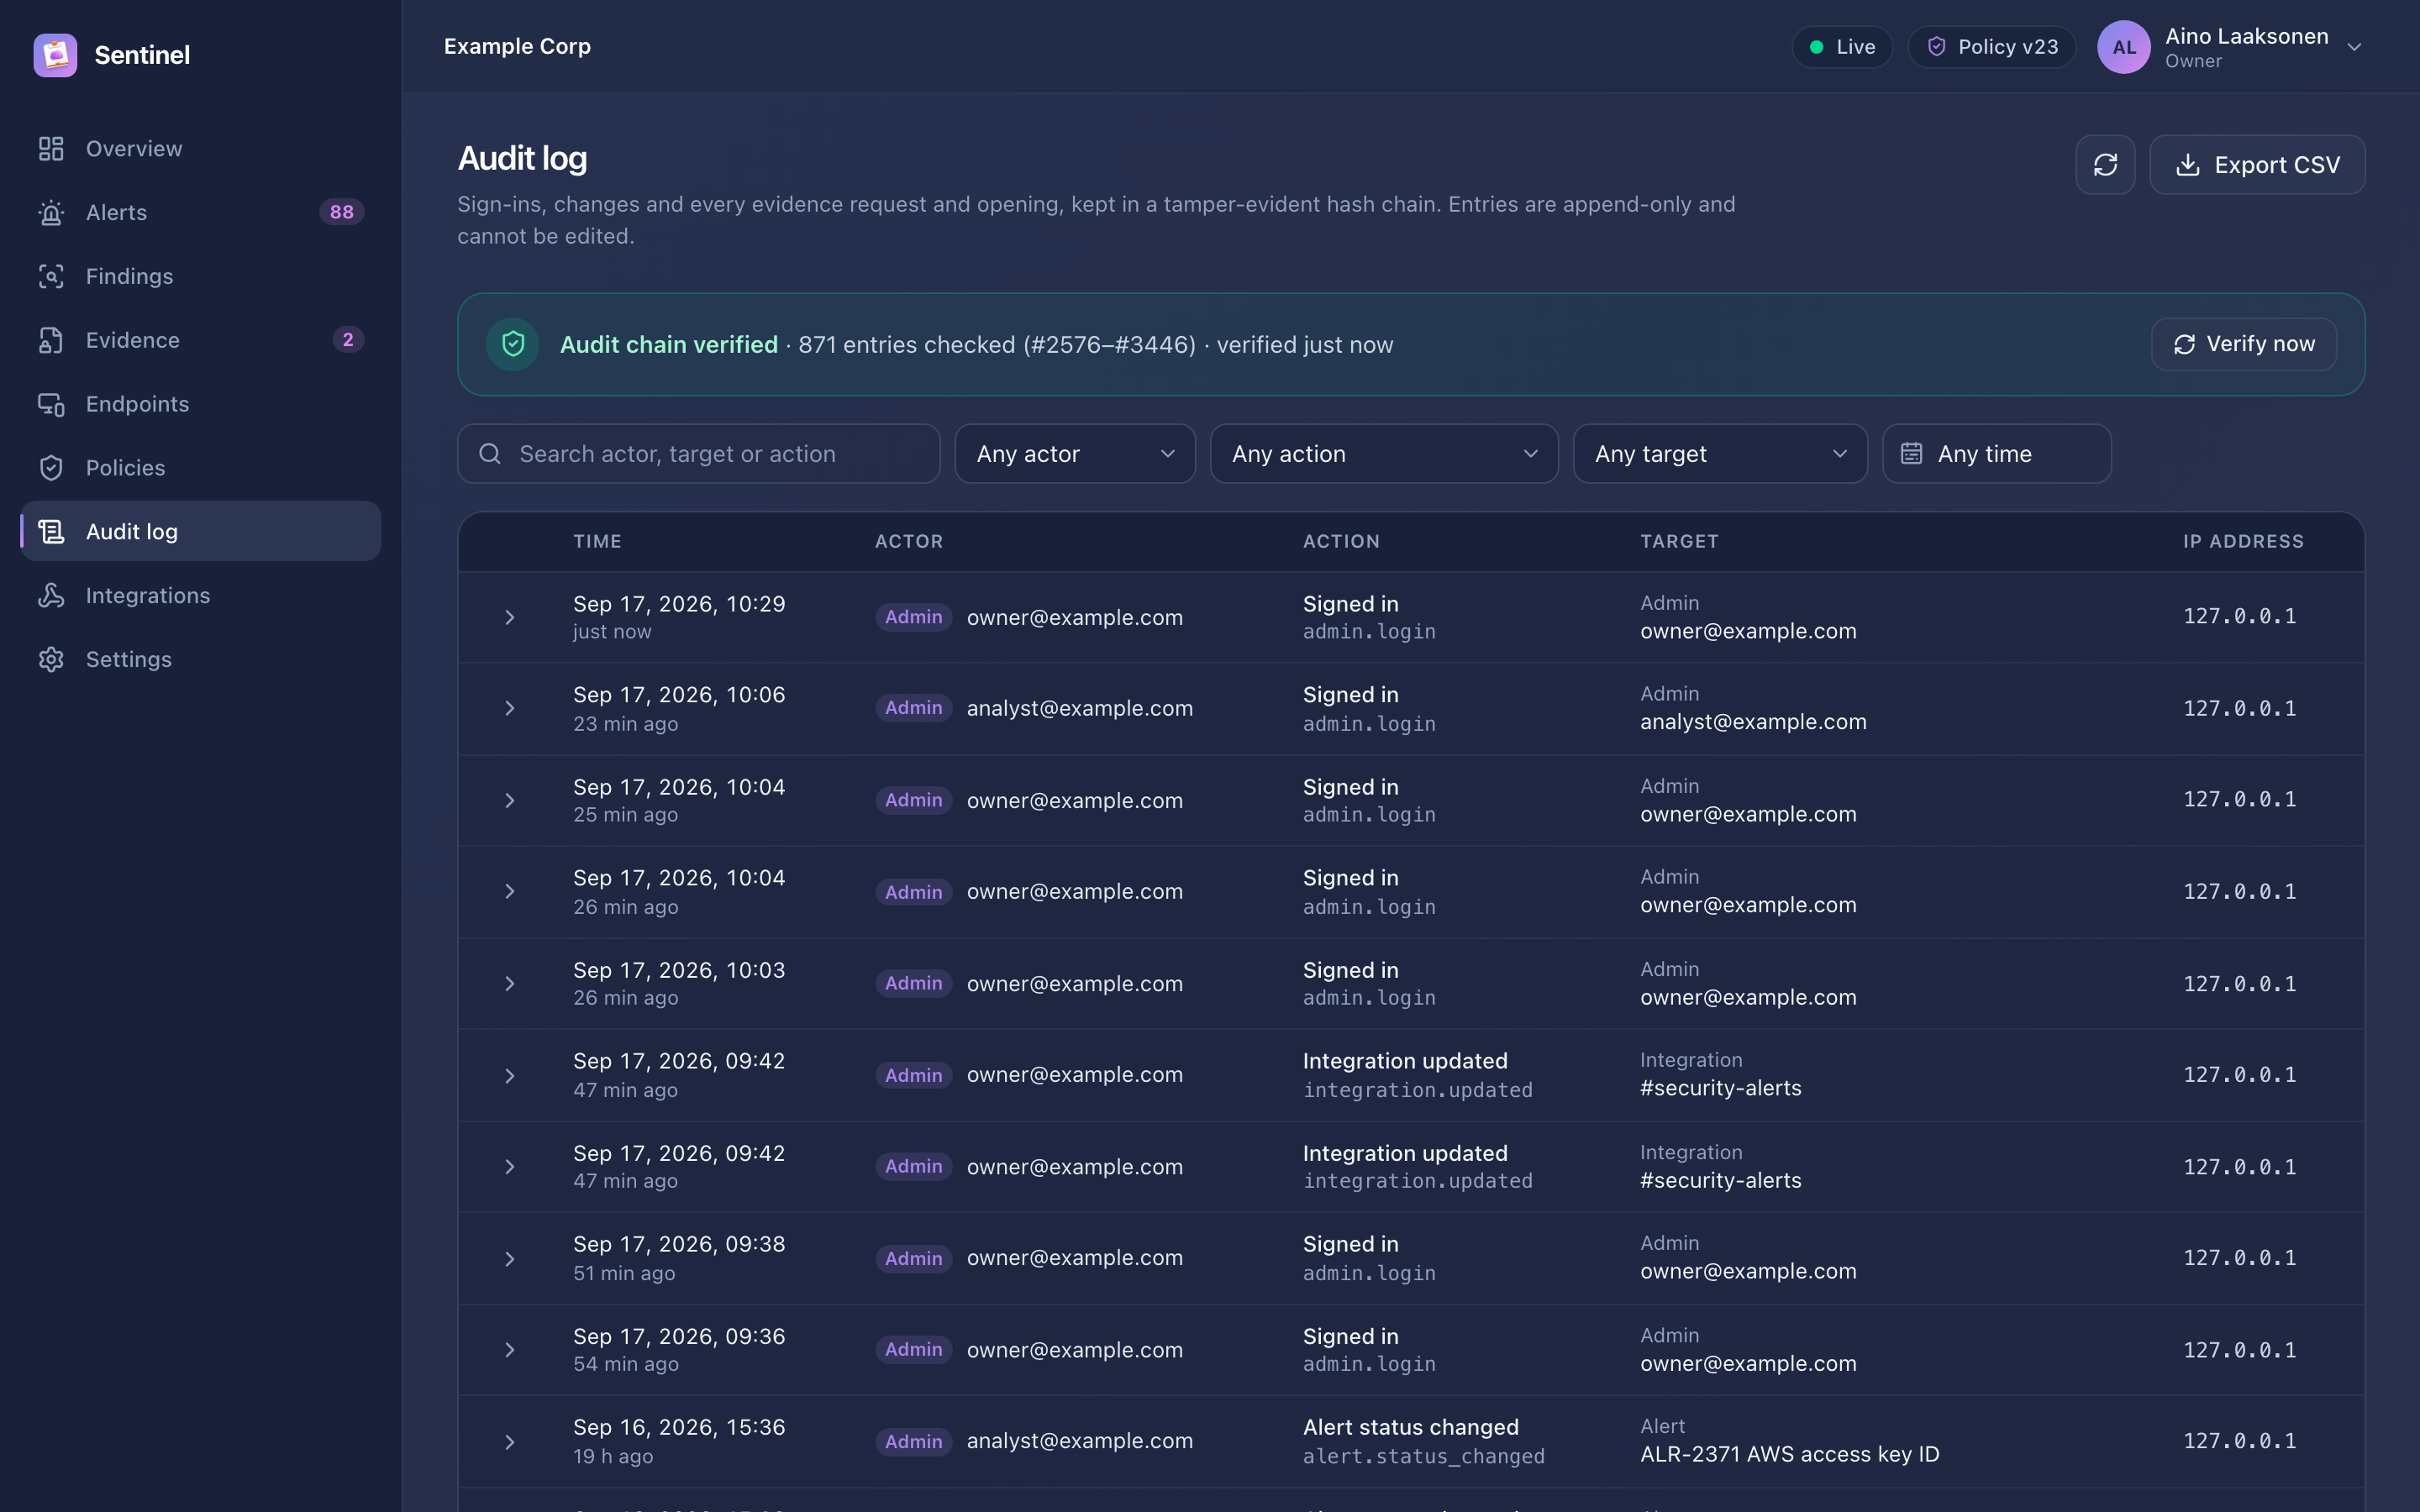
Every administrative action in Sentinel is recorded in a tamper-evident audit log:
- sign-ins, failed sign-ins and lockouts;
- rule, policy and setting changes;
- enrollment, revocation and suspension;
- alert triage;
- evidence requests, uploads and openings, including the stated purpose;
- key and license operations.
Chain verification
Each entry is chained to the previous one with an HMAC, so changing, deleting or reordering entries outside Sentinel breaks the chain.
The Audit log page verifies the entire chain and shows the result in a banner. If verification fails, the banner names the first entry that does not match.
CAUTION
A broken chain means the database was changed outside Sentinel, or a database backup was restored with a different key file. Preserve the database as it is and contact enterprise@klipsu.com.
Search and export
Filter by actor, action (for example every action starting with evidence.), target and time range. Export CSV downloads the filtered entries (up to 100,000 rows) for your records or your SIEM. Values that spreadsheet applications could interpret as formulas are escaped.
Owners, admins and auditors can verify and export the audit log. With pseudonymisation enabled, analysts see pseudonyms instead of employees' names and email addresses.